Where each product stands out — and what to check
Option 1Vanta
Best for: Security compliance and trust programs
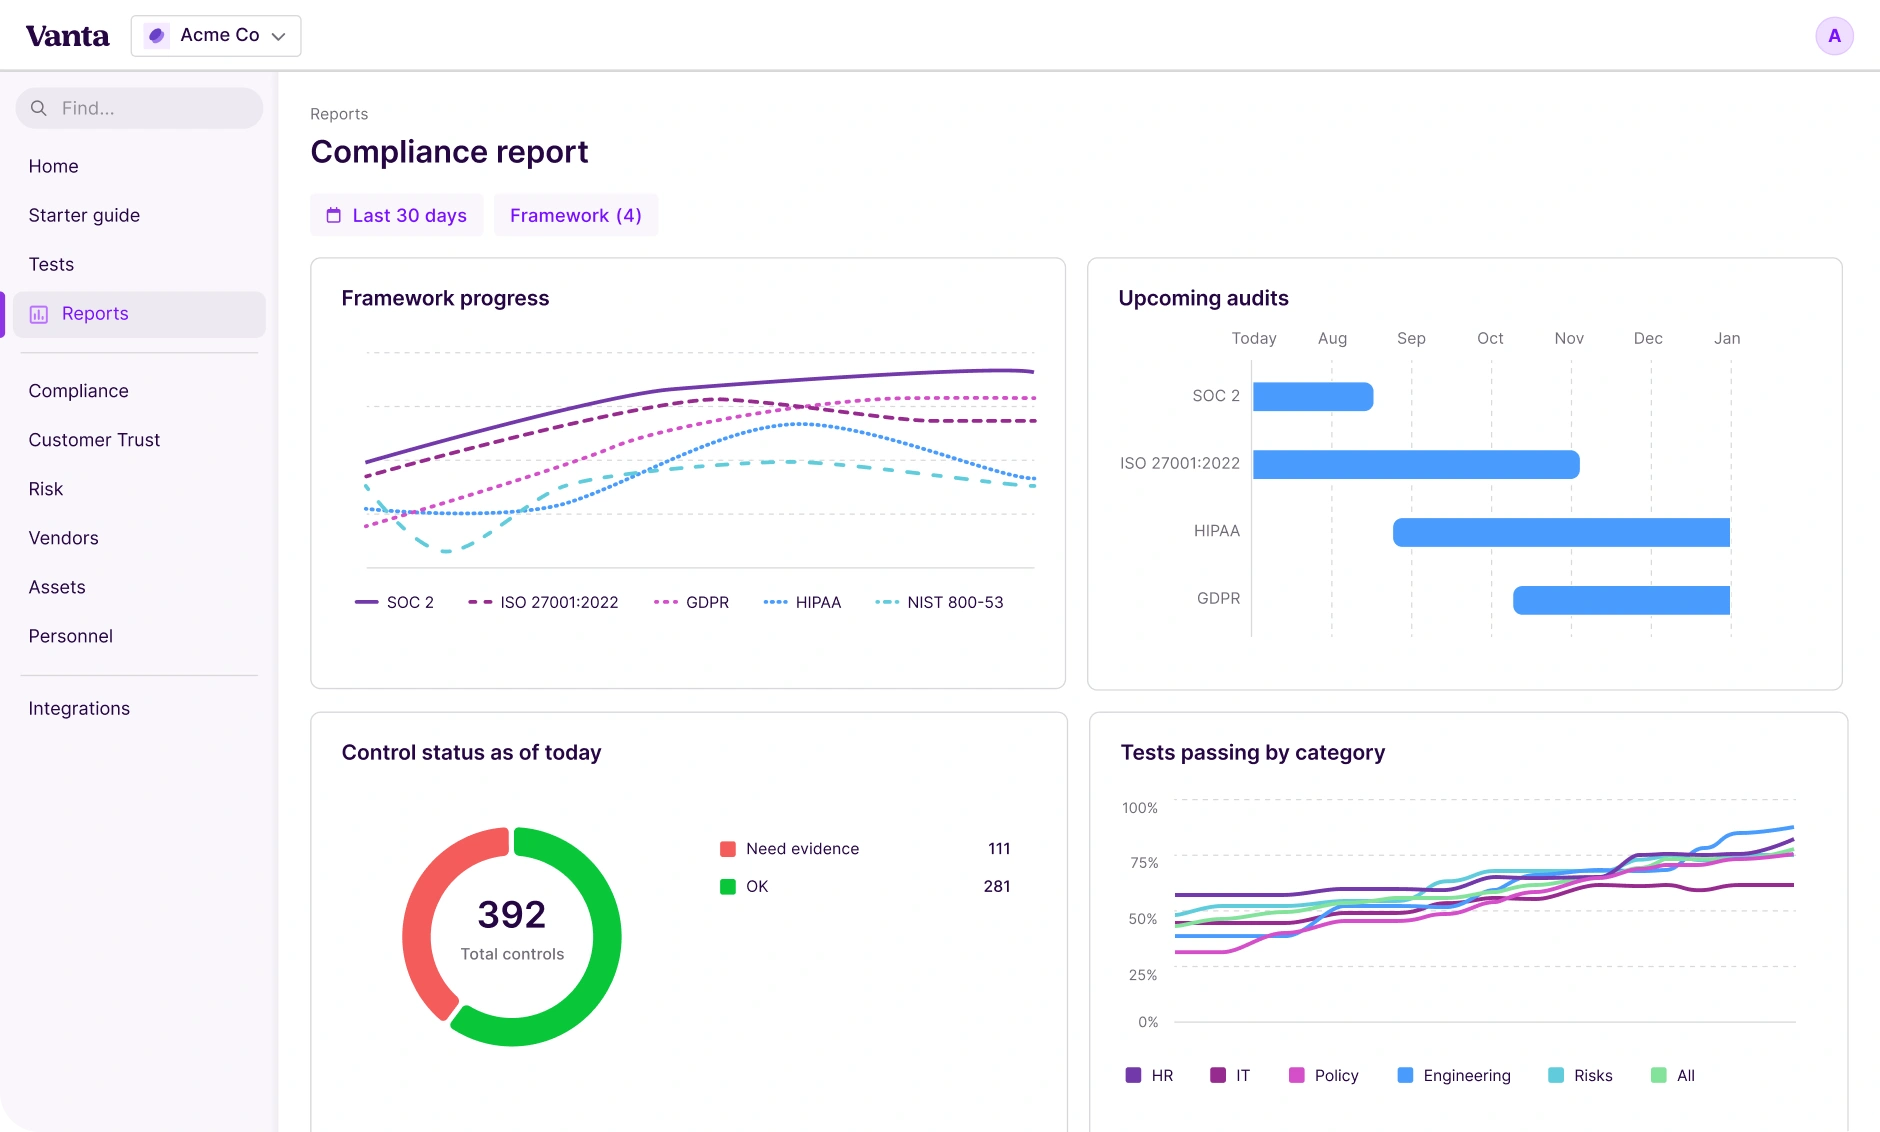
Vanta integrates with common cloud and identity systems to help teams collect evidence, monitor technical checks and prepare for assessments such as SOC 2 and ISO 27001. It is often most compelling when audit readiness is a recurring workload.
Trade-off to investigateAutomation does not replace strong policies or operating security controls. Confirm framework and module coverage in the quoted tier.
Ask for this live demoDisable access for a departing employee, observe the resulting control signal and locate auditor-ready evidence.
Option 2Drata
Best for: Continuous evidence collection and control monitoring
Drata focuses on connecting technical systems to control evidence and tracking compliance work through repeated audits. It suits teams willing to maintain accountable owners while automating the collection they would otherwise perform manually.
Trade-off to investigateUnsupported systems, manual people/process controls and exception workflows still require real effort.
Ask for this live demoShow a failed identity control, assign remediation, collect fresh evidence and prepare an auditor export.
Option 3Secureframe
Best for: Growing teams managing multiple frameworks
Secureframe organizes requirements, common controls, monitoring and remediation workflows. Mapping a single control to several standards can reduce repetitive compliance documentation for teams expanding beyond a first audit.
Trade-off to investigateVerify control customization, included frameworks, advisor services and integration depth per plan.
Ask for this live demoMap one access-review control across two frameworks and show the owner and related remediation items.
Option 4LogicGate Risk Cloud
Best for: Configurable enterprise risk and GRC workflows
LogicGate Risk Cloud is better assessed as a flexible GRC platform for teams formalizing risks, control testing, third-party assessments and governance operations. It can suit complex process owners beyond a single security audit.
Trade-off to investigateFlexibility also means configuration and program design. Validate workflow ownership, reporting and administrator workload.
Ask for this live demoCreate a vendor risk review with control exceptions, multiple reviewers and board-level reporting.
Option 5OneTrust
Best for: Broader privacy, third-party and risk governance
OneTrust spans privacy, risk and governance use cases. It may fit organizations coordinating privacy assessments, vendor obligations and compliance teams, especially when processes cross legal, security and procurement.
Trade-off to investigateA suite can be modular: identify the exact solution you require, the integrations and the administration needed.
Ask for this live demoRoute a supplier privacy assessment to legal and security, record remediation, and track the decision.
How to evaluate the shortlist
01 · Decide whether you need audit evidence automation, enterprise GRC, privacy operations or a combination.
02 · Map the actual control owners, evidence systems and framework overlap before demos.
03 · Test exceptions and remediation; dashboards full of green checks are not the whole compliance program.
04 · Request evidence of auditor collaboration, access boundaries and historical control status.
One test that exposes real differences
Demo scenario: an employee retains cloud access after termination, one evidence integration stops syncing, and a supplier fails a privacy check. Ask each product to flag what it can detect, route remediation to the correct owner and demonstrate a complete audit trail for the outcome.
Pricing and implementation: budget for the complete workflow
Compare charges for frameworks, number of entities, assets, connectors, audit support, trust centers, third-party risk modules and implementation. Add auditor and internal staff time; platform costs are only one part of an audit program.
Frequently asked questions
Can compliance software guarantee a favorable SOC 2 audit outcome?
No. SOC 2 results in an independent CPA firm's attestation report, not a certification. Software can collect evidence and highlight gaps, but it cannot guarantee the auditor's opinion.
What distinguishes Vanta or Drata from LogicGate?
The first group is often evaluated for technical compliance evidence and ongoing checks; LogicGate is a broader configurable GRC workflow product. Evaluate the actual work to be managed.
Why do control owners still matter?
Automated systems cannot approve every policy, investigate every exception or maintain every people process. Assigned owners are essential for trustworthy results.
Related buying resources
Sources and selection notes
Editorial assessment based on vendor-documented capabilities, use-case fit and workflow evaluation. This is not a hands-on benchmark or a user-review score. Vendor documentation: Vanta · Drata · Secureframe · LogicGate Risk Cloud · OneTrust. Screenshots illustrate one vendor and may differ from current releases.